Most network outages are not total failures. They usually come down to one bad cable, one failed port, one misconfigured gateway, or one access point that cannot keep up with client demand.
Cisco CCNA v1.1 (200-301)
Learn essential networking skills and gain hands-on experience in configuring, verifying, and troubleshooting real networks to advance your IT career.
Get this course on Udemy at the lowest price →Quick Answer
Network hardware is the physical equipment that moves data between devices, networks, and the internet. It includes network interface cards, switches, routers, modems, access points, and security appliances. Understanding these devices helps IT teams troubleshoot faster, design better networks, and isolate faults before they spread across the environment.
Definition
Network hardware is the collection of physical devices that connect endpoints, forward traffic, and extend communication across local and wide-area networks. It includes both endpoint components like a Network Interface and infrastructure devices such as switches, routers, and access points.
| Core Function | Physical connectivity, traffic forwarding, and network control |
|---|---|
| Primary OSI Layers | Layer 1, Layer 2, and Layer 3 |
| Common Devices | NICs, switches, routers, modems, access points, firewalls |
| Typical Troubleshooting Focus | Power, cabling, link status, IP settings, gateway reachability |
| Enterprise Features | VLANs, PoE, QoS, link aggregation, port security |
| Related Skill Areas | Campus networking, branch networking, wireless, and security design |
| Best Fit For | Home, SMB, campus, branch, and enterprise networks |
What Network Hardware Devices Are and Why They Matter
Network hardware devices are the physical components that move traffic, connect systems, and keep communication flowing across a network. That sounds basic, but the business impact is anything but basic. When hardware fails, users lose access to shared files, internet services, printers, voice systems, cloud apps, and security monitoring.
The cleanest way to think about the definition of network hardware is to split it into two groups. Endpoint hardware lives on the device itself, such as a NIC inside a laptop or server. Infrastructure hardware sits between devices, such as switches, routers, firewalls, access points, and network tap devices used for visibility and analysis.
Why it matters in real work
If you can identify which device owns the failure point, you stop guessing. A bad cable points to the physical layer, a dead switch port points to Layer 2, and a broken default gateway can stop traffic leaving the subnet. That is why hardware knowledge is so important in support roles, especially when you need to isolate whether the issue is local, segment-wide, or upstream.
For a deeper grounding in troubleshooting methods, the BLS notes that network and computer systems administrators are expected to maintain and troubleshoot networks as part of core job duties; see the U.S. Bureau of Labor Statistics. Vendor documentation also reinforces this practical skill set, including Cisco’s guidance on Cisco® networking devices and Microsoft® guidance on device connectivity through Microsoft Learn.
Most “the network is down” tickets are really one broken link in a chain. The faster you identify the link, the faster you restore service.
Why hardware basics improve design
Hardware choices affect speed, reliability, security, and scalability. A small office might get by with an all-in-one device. A campus or branch network usually needs separate switching, routing, wireless, and security functions to avoid bottlenecks and single points of failure. That separation is a core reason the Cisco CCNA v1.1 (200-301) course remains relevant for practitioners who need to configure and troubleshoot real environments.
As of 2026, IT teams are expected to support a wider mix of wired, wireless, cloud-connected, and security-aware hardware than ever before. The core devices have not changed much, but the way they are deployed absolutely has.
How Network Hardware Fits Into the OSI Model
The OSI model is a troubleshooting shortcut because it helps you map symptoms to a likely failure point. Most network hardware operates primarily at Layer 1, Layer 2, or Layer 3, and that layer focus tells you what to check first.
Layer 1 covers signaling, cabling, ports, and electrical or optical transmission. Layer 2 handles frames, MAC addresses, and local forwarding. Layer 3 introduces IP addressing and routing between networks. Many devices blur those boundaries, but the OSI model still gives you a practical way to isolate where communication breaks down.
- Layer 1 devices: Cables, transceivers, repeaters, and physical ports.
- Layer 2 devices: Switches, bridges, and wireless access points.
- Layer 3 devices: Routers and some multilayer switches.
- Cross-layer devices: Firewalls, gateways, and network tap devices that monitor or control traffic.
Why layer mapping helps troubleshooting
If a laptop shows “connected” but cannot reach anything beyond the local subnet, the NIC may be fine and the fault may sit at Layer 3. If only one printer is down, the problem may be a single switch port, not the router. If every wired device on one floor fails, that points you toward a switch stack, uplink, or power problem.
This is also where campus and branch networking becomes clearer. In a campus network, Layer 2 segmentation and Layer 3 routing often work together across multiple access closets and distribution layers. In a branch network, a smaller number of devices may handle the same duties, but the troubleshooting logic does not change.
For standards-based troubleshooting and network visibility concepts, useful references include the Cisco documentation ecosystem, the National Institute of Standards and Technology guidance on secure architecture, and the MITRE ATT&CK knowledge base for understanding how attackers move through network infrastructure.
How Does Network Hardware Work?
Network hardware works by taking a signal, frame, or packet and moving it to the next correct point in the path. The process depends on the device type, but the basic pattern is always the same: identify the source, inspect the destination, apply policy if needed, and forward traffic onward.
- Endpoints generate traffic. A NIC in a laptop, server, printer, or IP phone creates the initial network connection.
- Local devices forward frames. A switch reads MAC addresses and sends traffic only to the right port instead of flooding every connected device.
- Routers make path decisions. A router examines IP addresses and sends packets toward the correct next hop or internet connection.
- Edge devices translate or filter. Modems, gateways, and firewalls shape how traffic enters, exits, or passes through the environment.
- Wireless hardware bridges clients. Access points connect Wi-Fi devices to wired infrastructure.
What makes this practical
The mechanism matters because different failures produce different symptoms. A switch port problem usually affects one device or one small group. A router issue can cut off internet access while internal traffic still works. A wireless access point issue can hit only mobile users on one coverage area. Once you know how the traffic is supposed to flow, you can test the exact point where it stops.
This same logic applies whether you are handling a home office setup or can you explain the role of network hardware in campus and branch networking. The path is different, but the diagnostic method is the same: trace the path, confirm each hop, and isolate the break.
Pro Tip
When you troubleshoot, start with the device closest to the user and move outward. That approach avoids blaming the router for a cable failure three feet away.
Network Interface Cards: The Device That Connects Endpoints to the Network
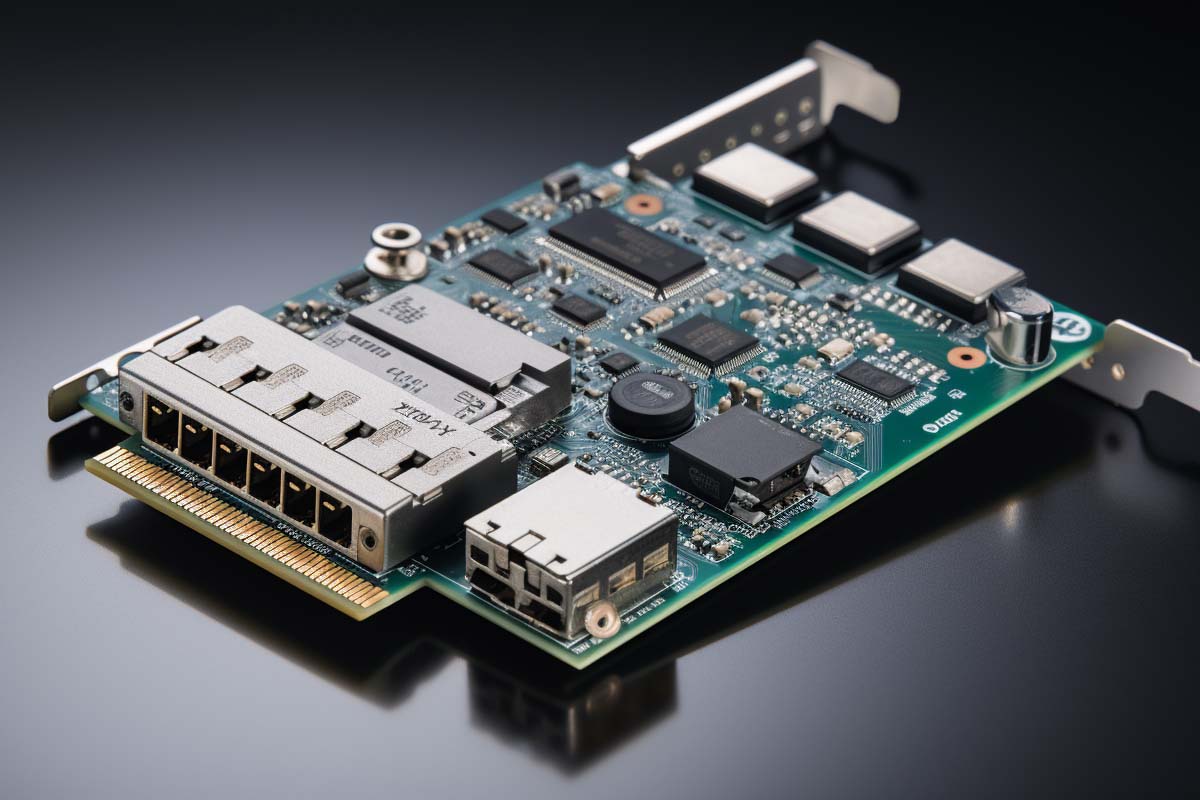
A network interface card (NIC) is the hardware that gives a device access to a network. It may be built into the motherboard, installed as an expansion card, or provided as a wireless adapter. Without a NIC, the endpoint has no way to create a usable network connection.
NICs appear in desktops, laptops, servers, printers, VoIP phones, surveillance systems, industrial gear, and many other connected devices. Wired NICs use Ethernet ports and cabling. Wireless NICs use radio frequencies to join a Wi-Fi network.
What to check on a NIC
- MAC address: The unique hardware address used for local network communication.
- Link status: Whether the interface is up, down, or negotiating speed.
- Driver support: Whether the operating system has the correct driver loaded.
- Speed negotiation: Whether the adapter and switch agree on 1 Gbps, 10 Gbps, or another supported speed.
- Interface health: Whether the port is physically damaged, disabled, or erroring.
NIC problems often masquerade as larger outages. A user might say “the network is down,” but the real issue could be a disabled interface, a bad driver, or a faulty cable at one desk. That is why first-line troubleshooting begins locally before you escalate to the switch or router.
For endpoint behavior and driver-level support, official documentation is the best reference point. Microsoft Learn and Cisco documentation both provide practical guidance for verifying connectivity, and IETF standards documents explain how Ethernet and IP traffic behave across interfaces.
Switches: The Traffic Directors of a Local Network
A switch is a Layer 2 device that forwards traffic between devices on the same local network. It learns which MAC addresses sit on which ports, then sends frames only where they need to go. That is much more efficient than older shared-media designs that repeated every signal to every port.
In practical terms, switches are the backbone of most office, campus, and branch LANs. They connect PCs, printers, servers, access points, phones, and sometimes cameras. If you want to understand devices in a network, switches are usually the best place to start.
Common switch types
| Unmanaged switch | Simple plug-and-play device for small environments with minimal control requirements. |
|---|---|
| Managed switch | Supports VLANs, monitoring, security controls, and more detailed traffic management. |
| Smart switch | Sits between unmanaged and fully managed, offering limited configuration and visibility. |
Why switches matter beyond connectivity
Modern switches do more than move frames. They often support VLANs for logical segmentation, Power over Ethernet (PoE) for phones and cameras, link aggregation for higher aggregate bandwidth, and port security to reduce unauthorized device access. These features are standard in enterprise environments because they improve both control and operational efficiency.
This is also where the search question can you tell me which network equipment has good usability? gets a practical answer: unmanaged switches are easiest to use, but managed switches are far more useful when you need visibility, segmentation, or troubleshooting features. Usability is not just simplicity; it is whether the device gives you the control you need without unnecessary complexity.
For switching architecture and enterprise features, Cisco’s official network documentation is the strongest product-level reference. For segmentation and control concepts, NIST guidance on secure network design is also useful.
Routers: Connecting Different Networks and Controlling Traffic Flow
A router is a Layer 3 device that moves traffic between separate networks. It decides where packets should go based on IP addressing and routing information. If the switch is the local traffic director, the router is the device that gets traffic out of the local neighborhood and toward another network or the internet.
In homes and offices, the router is often the device that hands out internet access and manages the default gateway. In enterprise environments, routers may sit at the edge, between sites, or inside the core depending on the design.
Key router functions
- Routing decisions: Select the next hop for outbound packets.
- Default gateway role: Provide the path off the local subnet.
- NAT: Translate private addresses to public-facing addresses at the edge.
- Basic filtering: Allow or block traffic based on simple policy rules.
- Route selection: Choose the best path when multiple paths exist.
A router failure often looks like “the internet is down,” but that description can be misleading. Internal communication may still work perfectly. Users can reach file shares, printers, and local servers while losing access to external websites and cloud services because the router or upstream link is the only broken piece.
For routing concepts and internet edge behavior, Cisco and the IETF remain the main technical references. If you are building practical skills for CCNA-level troubleshooting, router behavior is one of the highest-value topics to master.
Modems, Internet Handoffs, and the Edge of the Network
A modem converts or terminates the signal used by an internet service provider into a form your network can use. Depending on the access method, this might mean cable, DSL, fiber, or another WAN handoff. The device at the edge is often blamed for outages that actually come from the ISP side, so knowing how to test it matters.
A standalone modem does one job: provide a service handoff. A modem-router combination does that job plus routing, NAT, and sometimes Wi-Fi. That convenience is fine for many small environments, but it can make troubleshooting harder because multiple functions live in one box.
How to tell inside from outside
- Check whether the LAN side still works.
- Ping the default gateway to confirm local routing.
- Test access to a public IP address to separate DNS issues from connectivity issues.
- Verify modem status lights or provider handoff indicators.
- Ask whether other customers on the same ISP circuit are reporting the same issue.
The difference between internal and external failure is crucial. If users can reach local resources but not the internet, the modem, router, or WAN circuit becomes a prime suspect. If nothing on the LAN works, the problem is probably closer to the switch, NIC, or cabling.
For WAN-edge design and service handoff concepts, consult official ISP and vendor documentation whenever possible. For broader service management and resilience planning, NIST and CISA guidance can help you think about dependencies and external risk.
Wireless Access Points: Extending Connectivity Without Cables
A wireless access point (AP) is a device that bridges wired network infrastructure to wireless clients. It is not the same thing as a router with built-in Wi-Fi, although consumer products often combine both roles into one box. In enterprise environments, access points are usually dedicated devices managed centrally.
APs connect laptops, phones, tablets, scanners, printers, and IoT devices to the network. They are especially important when mobility, density, or building layout makes cabling impractical.
What affects AP performance
- Coverage: Whether the signal reaches the users who need it.
- Interference: Competing RF signals, walls, and metal structures.
- Placement: Ceiling height, distance, and physical obstructions.
- Client density: How many devices share the same AP radio resources.
- Roaming behavior: How smoothly clients move between APs.
AP issues often show up as weak signal, slow throughput, disconnects, or a user who can connect in one room but not another. In business environments, those symptoms are often caused by poor placement or too many clients on too few access points.
Cloud-managed and controller-based wireless systems have made AP administration easier, but the fundamentals still matter. You still need to plan channel use, placement, and power correctly. For wireless design and security, Cisco, IEEE 802.11 standards, and NIST are the best places to verify technical behavior.
Hubs, Bridges, Repeaters, and Why Older Devices Still Matter Conceptually
Hubs, bridges, and repeaters are older device types, but they still matter because they explain why modern network hardware works the way it does. A hub repeats traffic to all ports. A bridge filters traffic between segments. A repeater regenerates signals so they can travel farther.
Hubs are mostly obsolete because they create unnecessary traffic and collisions. Switches replaced them by learning where devices live and forwarding traffic more intelligently. That historical shift explains a lot about why modern LANs perform better.
Why learners should still know them
- Hub: Useful for understanding shared collision domains and why flooding is inefficient.
- Bridge: Useful for understanding traffic filtering between segments.
- Repeater: Useful for understanding signal regeneration over distance.
If you are studying for networking fundamentals, these older devices give useful context. They explain how the industry moved from shared, noisy networks to switched and segmented designs. That context also makes modern troubleshooting more intuitive because you understand why the network behaves the way it does.
For historical and standards-based context, the IETF and IEEE are the most credible references for Ethernet and wireless behavior.
What Is a Gateway in Network Hardware?
A gateway is a device or function that connects dissimilar networks or translates between systems that do not speak exactly the same protocol or format. In everyday networking, people often use the term loosely to mean the default gateway, which is the router address a device uses to leave its local subnet.
That distinction matters. A gateway can be a router, a security appliance, a protocol translator, or another boundary function. A default gateway is specifically the next hop for outbound traffic from a host on a local network.
Where gateways show up
- Branch offices: To connect local users to corporate resources.
- Cloud access: To route traffic between on-premises and hosted services.
- Legacy integrations: To bridge older systems with newer platforms.
- Specialized environments: To translate between industrial, voice, or IoT systems.
Gateway failures usually show up as reachability problems, not total network collapse. Users may still see a Wi-Fi connection or a LAN link, but they cannot get to the destination they need. That symptom often points to translation, routing, or boundary policy rather than a core switching failure.
For gateway security and boundary control, NIST and CISA guidance are strong references. If you work in environments that need stronger access control, gateway behavior often intersects with firewall policy and segmentation strategy.
Security Roles of Network Hardware Devices
Network security hardware is not limited to standalone firewalls. Security is built into device placement, traffic segmentation, port controls, and visibility tools that watch what is moving through the network. Hardware decisions can either reduce exposure or make every other security control harder to enforce.
A firewall filters traffic based on policy. A switch can limit unauthorized access with port security and VLAN design. A router can constrain paths and separate networks. An access point can enforce authentication and isolate guest traffic. These controls work together, and each one adds a layer of defense.
Security is not only a software problem. The physical network design can either enforce or undermine your security policy.
Modern security-aware devices and features
- Firewalls: Filter allowed and denied traffic at the network edge or internally.
- Intrusion detection and prevention systems: Inspect traffic for malicious patterns.
- Segmentation: Reduce the blast radius of a compromised device.
- Port security: Limit which devices can connect to a switch port.
- Network tap devices: Provide passive visibility into security events and packet flow.
When people ask about security devices in line with network traffic, the real answer is that visibility and control both matter. You need devices that block bad traffic and tools that show you what is actually happening on the wire. Network packet brokers can also help distribute mirrored traffic to monitoring and security tools without overloading a single analyzer.
For security architecture and threat visibility, NIST, CISA, and MITRE ATT&CK provide the most practical public references. For network design that supports monitoring, the Cisco CCNA v1.1 (200-301) course is a good fit because it reinforces how traffic actually flows before you try to secure it.
Modern Enterprise Features That Shape Network Performance
Modern network hardware is expected to do more than connect devices. It also needs to segment traffic, support voice and video, simplify power delivery, and help teams maintain performance at scale. That is why enterprise equipment includes features that are unnecessary in a basic home setup.
Features that matter most
- VLANs: Separate traffic logically without needing separate physical switches for every group.
- PoE: Deliver power and data over the same Ethernet cable for phones, cameras, and APs.
- QoS: Prioritize latency-sensitive traffic such as voice and video.
- Link aggregation: Combine multiple physical links for more bandwidth and resilience.
- Centralized management: Simplify changes across many devices and sites.
These features matter because traffic patterns are more complex than they were in older networks. One office switch may now support cloud access, VoIP, conferencing, wireless users, security monitoring, and building devices at the same time. Without segmentation and prioritization, performance drops quickly.
For standards and implementation details, Cisco, IEEE, and NIST are the best public sources. If you need to understand whether a feature is really useful, ask one question: does it improve throughput, reliability, performance, or operational control?
How to Troubleshoot Network Hardware Devices Step by Step
Layered troubleshooting is the fastest way to isolate hardware failures. Start at the physical layer, verify the endpoint, then move outward until you find the device or link that breaks the chain. Do not jump straight to the router just because users can’t reach the internet.
- Check power and cabling. Confirm the device is on, the cable is seated, and the port shows link lights.
- Verify the local interface. Check NIC status, Wi-Fi association, or switch port activity.
- Confirm addressing. Make sure the IP address, subnet mask, and default gateway are correct.
- Test local reachability. Ping the gateway, then test a known internal host.
- Move upstream. Check the switch uplink, router, WAN circuit, or ISP handoff.
Useful commands and checks
ipconfig /allorip addrto review interface addressing.pingto test basic reachability.tracertortracerouteto identify where traffic stops.show interfaceson switches and routers to inspect errors and link state.show vlanandshow mac address-tableto verify segmentation and port learning.
For anyone building real troubleshooting skill, this is the same logic used in enterprise support teams. It is also a core part of the hands-on skills reinforced in Cisco CCNA v1.1 (200-301), where the point is not memorizing device names but learning how to diagnose actual connectivity problems.
Common Failure Scenarios and What They Usually Mean
Failure patterns tell you more than vague user complaints ever will. A single dead cable usually affects one device. A bad switch port can take out one workstation or printer. A failed uplink can wipe out a whole segment. Once you recognize the pattern, you can narrow the cause much faster.
Typical symptoms and likely causes
- One device offline: Bad cable, NIC failure, disabled interface, wrong IP configuration.
- Many wired users affected: Switch failure, uplink failure, PoE issue, power loss.
- Internet only is down: Router, modem, DNS, or ISP problem.
- Wireless is weak or unstable: Interference, poor placement, overloaded AP, channel conflict.
- Some users isolated: Wrong VLAN, port security violation, ACL, or segmentation error.
One of the most common mistakes is assuming connectivity means correctness. A device can appear connected and still fail because it landed in the wrong VLAN, got the wrong static address, or lost access to its default gateway. Those are configuration issues, not physical failures, and they require a different fix.
For failure analysis, symptom mapping is often faster than packet capture. If the symptom is local, investigate local hardware. If the symptom is segment-wide, investigate switching or access-point design. If the symptom crosses networks, focus on the router, gateway, or ISP edge.
How Network Hardware Choices Differ by Environment
Network hardware selection changes based on scale, uptime expectations, security needs, and budget. A home office can often rely on one integrated router, a few endpoints, and maybe a small switch. A branch office usually needs separate switching, routing, and wireless planning. An enterprise campus needs redundancy, segmentation, monitoring, and centralized administration.
Environment-based differences
| Home or small office | Simple integrated devices, fewer ports, limited management, lower cost. |
|---|---|
| Branch office | Managed switching, reliable WAN edge, PoE, and consistent wireless coverage. |
| Enterprise campus | Redundant uplinks, VLANs, centralized monitoring, multiple APs, and security controls. |
As device counts grow, so does the need for managed infrastructure. More users mean more traffic. More wireless clients mean more airtime contention. More endpoints mean more support tickets. That is why planning for scalability is a hardware decision, not just a software one.
For workforce and growth context, the BLS Occupational Outlook Handbook remains a useful public source for networking job expectations, while CompTIA® workforce research helps explain the sustained need for practical infrastructure skills.
Current Trends and Emerging Directions in Network Hardware
Network hardware trends are moving toward software-driven control, but the physical devices still matter. SD-WAN changes how branch traffic is routed and prioritized. Network function virtualization reduces dependence on dedicated appliances. Cloud-managed networking makes administration easier across distributed sites.
What is changing
- SD-WAN: Uses policy and software control to steer traffic across multiple links.
- Network function virtualization: Replaces some dedicated hardware functions with software-based services.
- Cloud-managed networking: Centralizes monitoring and configuration across sites.
- Security visibility: More teams are adopting packet brokers and tap devices to support monitoring tools.
The important point is this: abstraction does not eliminate hardware fundamentals. Even the most advanced control plane still depends on links, interfaces, power, and forwarding devices underneath. If the switch port fails, the software logic does not matter.
For current architecture and operational guidance, NIST, Cisco, and vendor-specific product documentation are still the most reliable references. For threat-aware visibility, the use of network tap devices and network packet brokers continues to grow because teams need better access to traffic without disrupting production links.
Key Takeaway
- Network hardware is the physical layer of connectivity, and most outages are isolated to one device, port, or link.
- NICs connect endpoints, switches forward traffic locally, and routers move packets between networks.
- Modems, access points, and gateways sit at critical boundaries where problems often look bigger than they are.
- Security depends on both hardware placement and policy, not software alone.
- SD-WAN and virtualization are changing control, but they do not replace the need to understand how traffic moves on real equipment.
Cisco CCNA v1.1 (200-301)
Learn essential networking skills and gain hands-on experience in configuring, verifying, and troubleshooting real networks to advance your IT career.
Get this course on Udemy at the lowest price →Conclusion
Understanding network hardware devices makes troubleshooting faster, network design smarter, and security stronger. Once you know what each device does, you can stop guessing and start tracing the failure point with purpose.
The big roles are straightforward. NICs connect endpoints. Switches move traffic inside the LAN. Routers connect different networks. Modems provide the WAN handoff. Access points extend connectivity wirelessly. Gateways translate or bridge boundaries where needed.
That knowledge is still essential even as networks adopt SD-WAN, cloud management, and virtualization. The tools may change, but the fundamentals do not. If you want to build real confidence working with network hardware, keep practicing layer-based troubleshooting, study how devices interact, and connect those basics to real deployment scenarios.
For a practical next step, review the device behaviors covered here and apply them in a lab or production-safe environment. The more you can recognize the failure pattern, the faster you can restore service.
CompTIA®, Cisco®, Microsoft®, and NIST are referenced as part of official documentation and industry standards context.
